CUT THROUGH THE CVE NOISE — Explore the platform
VULNERABILITY INTELLIGENCE, REIMAGINED

Every vulnerability.
Only what matters.

Thousands of new vulnerabilities. One question that counts: Does this affect us? SeQurance connects threat intelligence to your actual software—so you can act with confidence, not guesswork.

✓ No credit card · Free plan available · Built for security teams

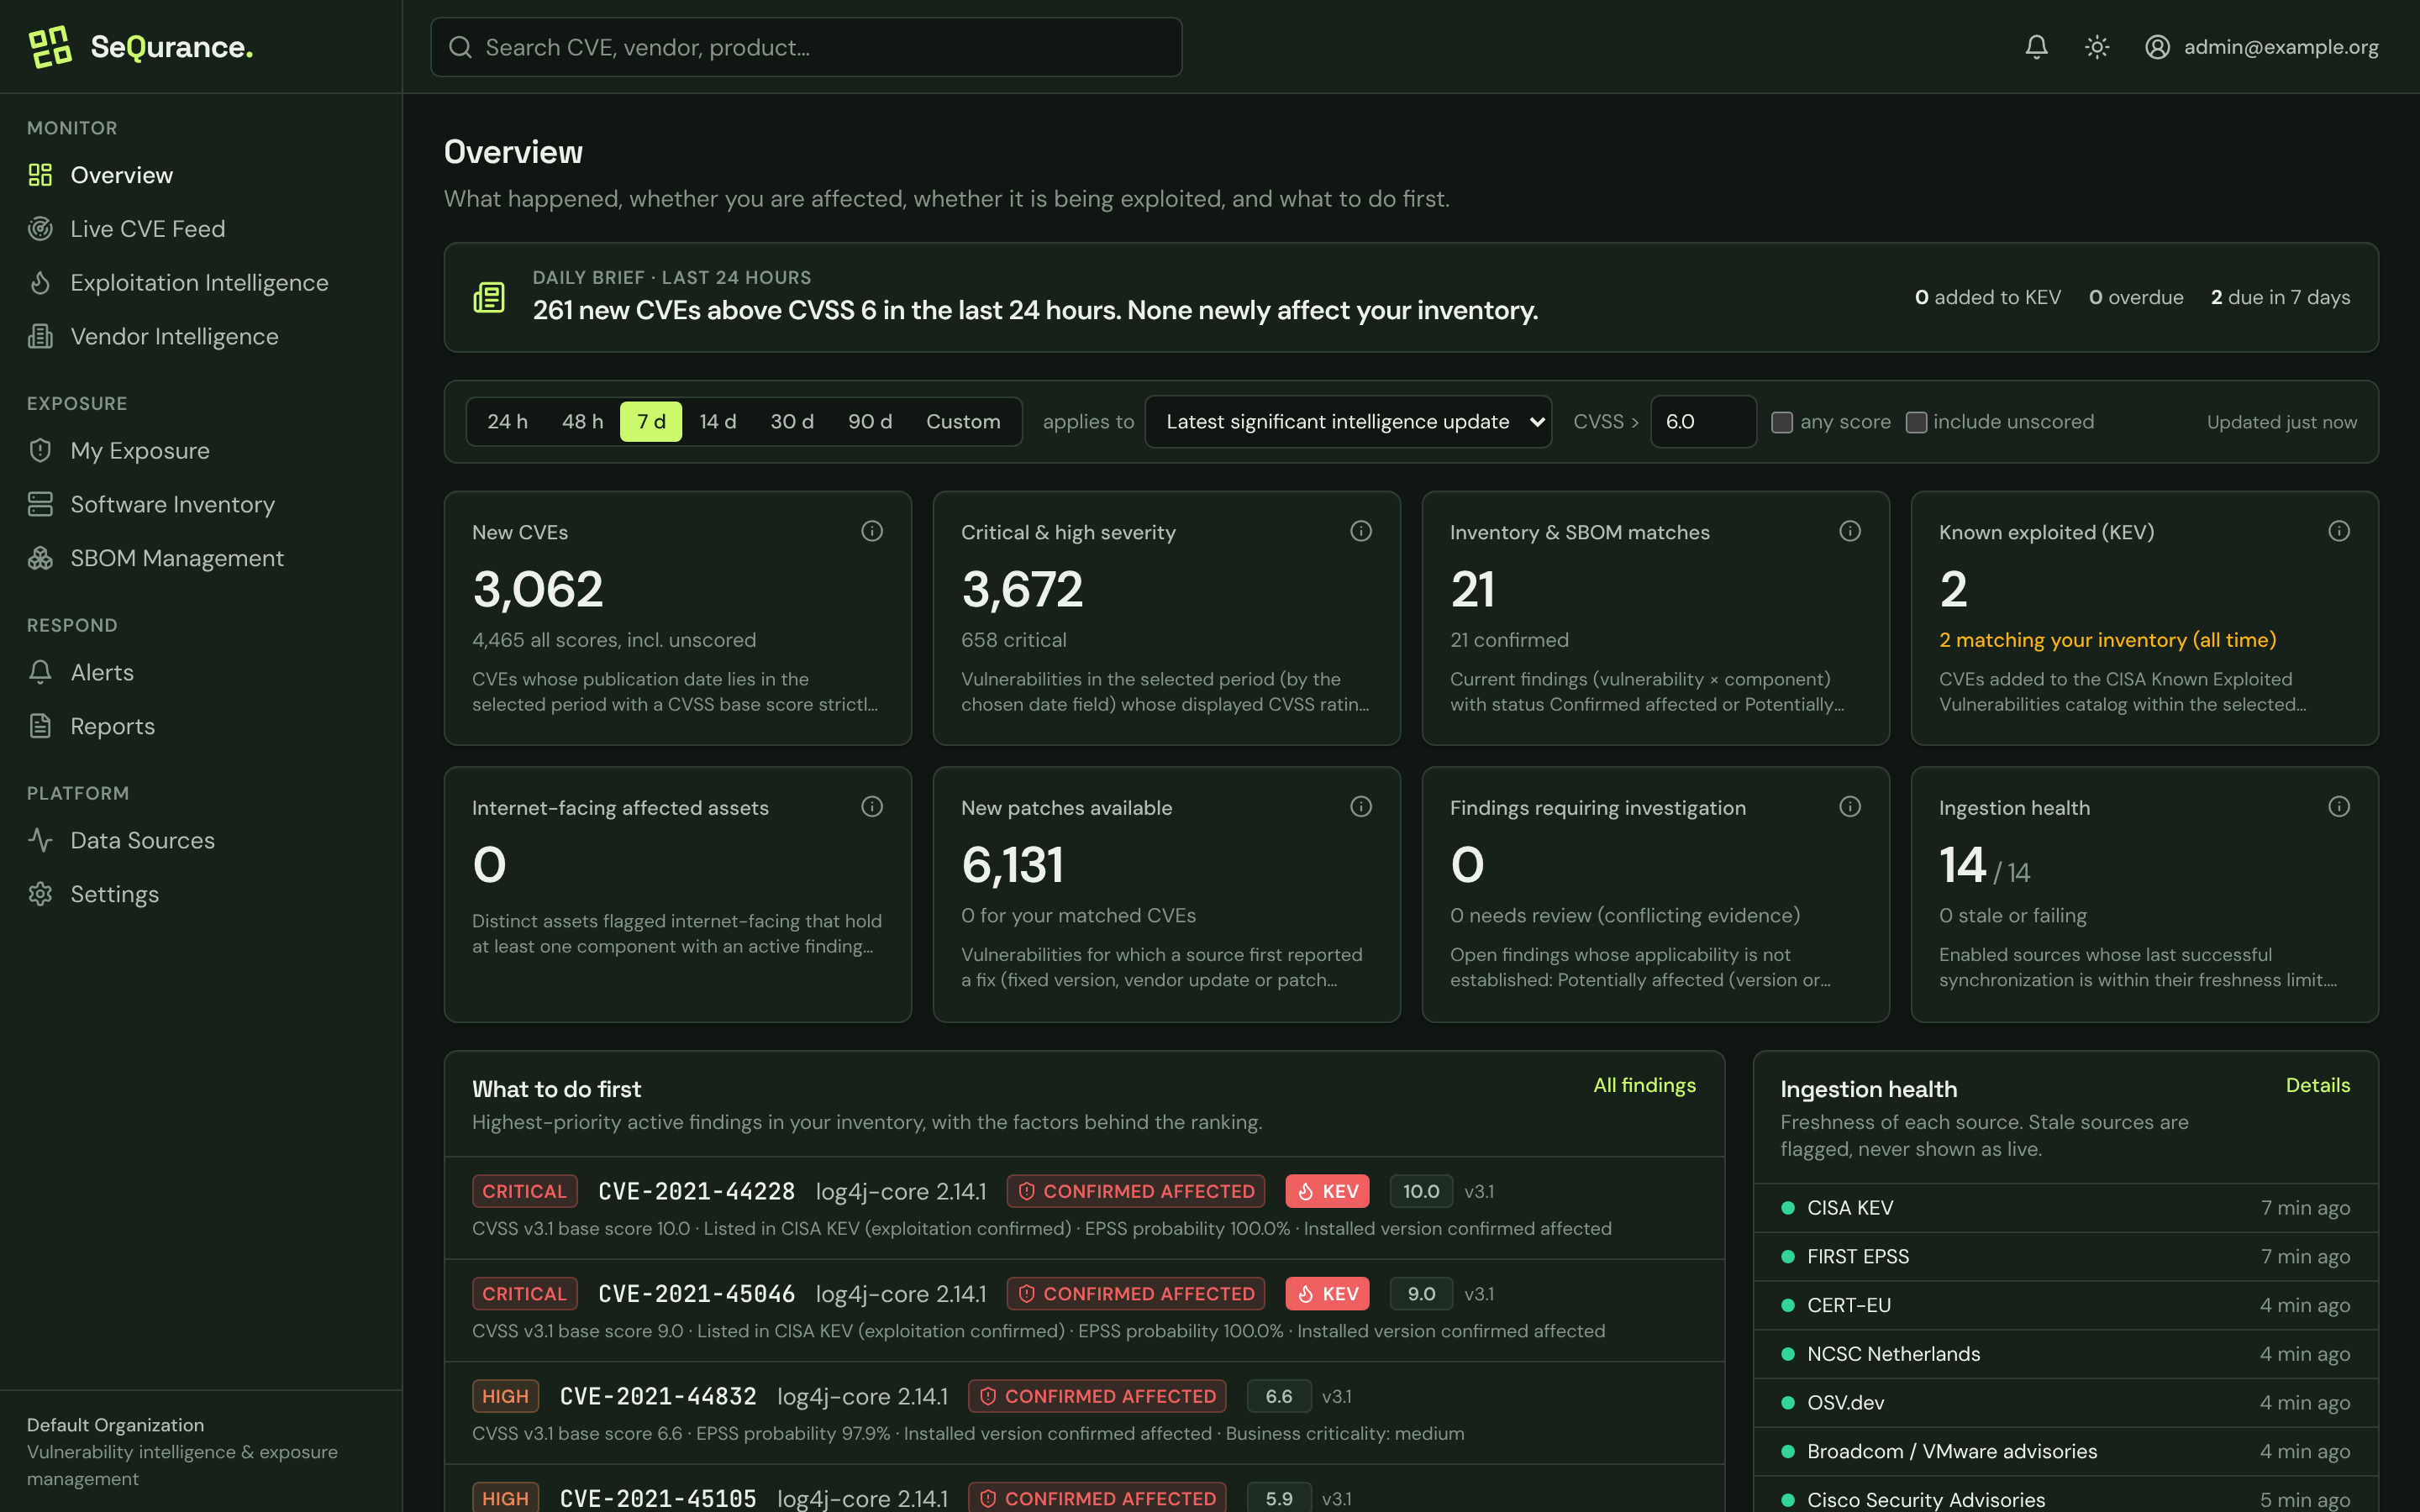
The SeQurance overview: daily brief, matches against your inventory and the most urgent findings
Signal, not noise.Evidence-backed prioritization
✓
INTELLIGENCE THAT CONNECTS THE DOTS
NVDCISA KEVEPSSOSVENISA EUVD
THE PROBLEM, SOLVED

Stop drowning in alerts.
Start knowing what matters.

Traditional vulnerability feeds tell you what exists. SeQurance helps you understand what actually affects your environment—and why.

01 / RELEVANCE

Your software.
Your exposure.

Add your inventory or upload CycloneDX and SPDX SBOMs. SeQurance matches new vulnerabilities against the products and components you actually use.

YOUR INVENTORYnginxTracked component
↔︎
INTELLIGENCENew advisoryVersion range evaluated
✓
Match evaluatedReasoning attached
02 / PRIORITIZATION

Severity isn't
the whole story.

See CVSS, EPSS, known exploitation and public exploit evidence as distinct signals. Make better calls with more context.

CVSS SEVERITY9.8 / 10
EPSS PROBABILITY72%
Known exploitation tracked separately
03 / ACCOUNTABILITY

Every decision.
Documented.

Capture status changes, overrides and remediation timelines. Give auditors the evidence they need without reconstructing the story.

✓Finding reviewed09:42
✓Fix implemented11:18
✓Evidence recorded11:22
HOW IT WORKS

From endless data
to a clear next move.

Three steps from unknown exposure to documented decisions.

01
INVENTORY CONNECTED
Application stack✓
CycloneDX SBOM✓
SPDX SBOM✓

Tell us what you run.

Add software and versions, organize your assets, or upload your SBOMs. Build a picture of your environment.

02
CONTINUOUS INTELLIGENCE

We connect the signals.

SeQurance monitors public vulnerability and exploitation sources and checks what matches your stack.

03
ACTIONABLE VERDICT
✓
ANALYSIS COMPLETEImpact understood.Evidence ready for review
Source referencesAttached ↗︎

Get an answer you trust.

See clear applicability verdicts, supporting sources, and remediation history—not unexplained scores.

BUILT FOR THE REAL WORLD

When someone asks
“How do you know?”
Have the answer.

Security isn't just detecting problems. It's explaining decisions, demonstrating action, and showing the full chain of evidence.

Transparent findings

See the affected product, version context and source behind every verdict.

Traceable remediation

Know when an issue was identified, addressed, and verified.

Audit-ready reporting

Turn your team's daily work into a clear record for stakeholders.

Build your evidence trail ↗︎
Finding evidenceDOCUMENTED
FINDING DETAILS / EXAMPLE

CVE-2026-48271

CRITICALMatch confirmed
Affected componentExample package 2.4.x
SourceVendor advisory ↗︎
Matching logicInstalled version within affected range
REMEDIATION TIMELINE

Finding identifiedAutomatically matched to inventory

Owner reviewed impactDecision and rationale saved

Resolution documentedEvidence added to audit log

Illustrative data ↗︎ Export evidence
CONNECTED CONTEXT

Multiple sources.
One clear picture.

Not another closed black box. Public vulnerability intelligence stays attributable to its source so your team can verify what it sees.

Start connecting the dots ↗︎
SeQurance.
NVDCISA KEVEPSSOSVENISA EUVDVendor advisories
SIMPLE START. ROOM TO GROW.

Start free.
Scale when you're ready.

Same intelligence, same matching engine. Choose the scale and operational tools your team needs.

FREE

Get clarity.

See what your own software is exposed to.

€0 / free
Start free
  • 1 user
  • 25 software components
  • 10 assets
  • 1 SBOM (up to 25 components each)
  • 2 alert rules
BUSINESS

Take control.

Many vendors, audits and a larger team.

€49.99 / month · excl. VAT
Choose Business
  • 25 users
  • 5,000 software components
  • 1,000 assets
  • 250 SBOMs (up to 20,000 components each)
  • 200 alert rules
  • 2 GB decision evidence storage
  • Vendor management for SBOMs
  • E-mail, Teams and webhook alerts
  • Daily brief by e-mail

Compare all plan limits and features ↗︎

PREFER TO KEEP IT IN-HOUSE?

Not ready to trust us?
Host it yourself.

Some teams need their data on their own servers, and that is fair. SeQurance can run there too. Ask us and we send you the source, or give you access to the repository, together with the terms. The hosted plans are for teams who would rather spend their time on vulnerabilities than on servers, updates and backups. It is the same engine either way.

Ask for the source
  • The same engine. The same matching, evidence and prioritization as the hosted service.
  • Your data stays with you. Everything runs on servers you control.
  • Ready to deploy. Docker Compose with install, update, backup and restore scripts.
  • Not included: the hosted extras, such as self-service sign-up and billing.
QUESTIONS, ANSWERED

Good questions.
Clear answers.

Still not sure where to start? Your free workspace is the simplest way to explore.

What is SeQurance, exactly? +

SeQurance is a vulnerability intelligence and exposure management platform. It maps reported vulnerabilities to the software and SBOMs you track, provides context for each match, and records remediation evidence.

Do I need an SBOM to get started? +

No. You can add products and versions manually, or upload a CycloneDX or SPDX SBOM.

Is the free plan really free? +

Yes. The Free plan has no subscription price and does not require a credit card. It has limits on users, components, assets and features.

Does SeQurance automatically fix vulnerabilities? +

No. It helps your team understand applicability, prioritize work, document decisions, and track remediation. Fixes remain under your control.

Can I run SeQurance myself? +

Yes, on request. Send us a message and we send you the source, or give you access to the repository, together with the terms. You then run it on your own servers and keep all data in-house. The hosted plans are for teams that would rather not run servers, updates and backups themselves.

Are paid subscriptions available? +

Yes. Pro and Business are monthly subscriptions, billed through Stripe. You can change or cancel at any time.

TAKE THE FIRST STEP

Know your exposure.
Own your response.

Move from vulnerability overload to evidence-backed decisions.

Create your free workspace ↗︎
No credit card required. Start with the software you already know.